ISO/IEC 42001 Consulting and AIMS Certification Readiness
AI governance, AI System Impact Assessment, vendor oversight, and audit-ready evidence
Pricoris provides ISO 42001 consulting services for organisations that use, procure, integrate, or develop AI systems. This includes GenAI tools, internal AI platforms, and AI-enabled SaaS products.
We help you implement an Artificial Intelligence Management System (AIMS) aligned to ISO/IEC 42001:2023. The focus is operational. The output is evidence. The goal is governance that stands up to audit and stakeholder scrutiny.
Facilitates Responsible AI Governing
Regulatory & Global Readiness
Build Trust and credibility
Enables Scalable AI Innovation
Get Consultant for Free:
Pricoris: Your Trusted ISO 42001 Consultant in India
Pricoris is a trusted ISO/IEC 42001:2023 consulting firm in India, helping organizations design and implement effective AI governance frameworks in line with ISO/IEC 42001:2023 requirements. Our consulting approach is practical, risk-focused, and tailored to match your organization’s AI maturity level. Our ISO/IEC 42001 Consulting Services in India include the following:
AI Readiness & Gap Assessment
We evaluate your existing AI systems, data flows, and governance structures to identify compliance gaps against ISO/IEC 42001 requirements.
AIMS Framework Design & Implementation
Our experts design and implement a customized AI Management System (AIMS), covering policies, controls, risk management, and operational processes.
AI Risk & Impact Assessments
We help identify, analyze, and mitigate AI risks related to bias, model drift, security threats, and ethical concerns.
Internal Audit & Certification Support
As experienced ISO/IEC 42001 consultants, we conduct internal audits and support your organization throughout the certification process until successful completion.
Benefits of ISO/IEC 42001
Regulatory & Legal Readiness
Prepares businesses to meet current and future AI laws, regulations, and standards.
Improved Risk Management
Identifies and reduces risks related to AI misuse, bias, security, and compliance.
Responsible AI Governance
Helps organizations manage AI systems in an ethical, transparent, and controlled manner.
Increased Trust & Credibility
Builds confidence among customers, partners, and stakeholders in AI-driven decisions.
Better Operational Efficiency
Creates structured AI processes that improve performance and reduce errors.
Competitive Advantage
Demonstrates commitment to responsible AI, helping organizations stand out in the market.
How We Make AI Controls Testable and Auditable
ISO 42001 requires traceability:
Traceability from identified risk through implemented controls to verifiable evidence and final governance decisions.”
AIMS scope and context
AI system inventory (Build / Buy / Boost)
AI policy and objectives
Roles, RACI, and governance forums
AI System Impact Assessment (AISIA)
AI risk Assessment and risk treatment
Annex A control applicability and SoA justification
AI lifecycle procedures
Vendor and AI SaaS oversight
Internal audit and management review readiness
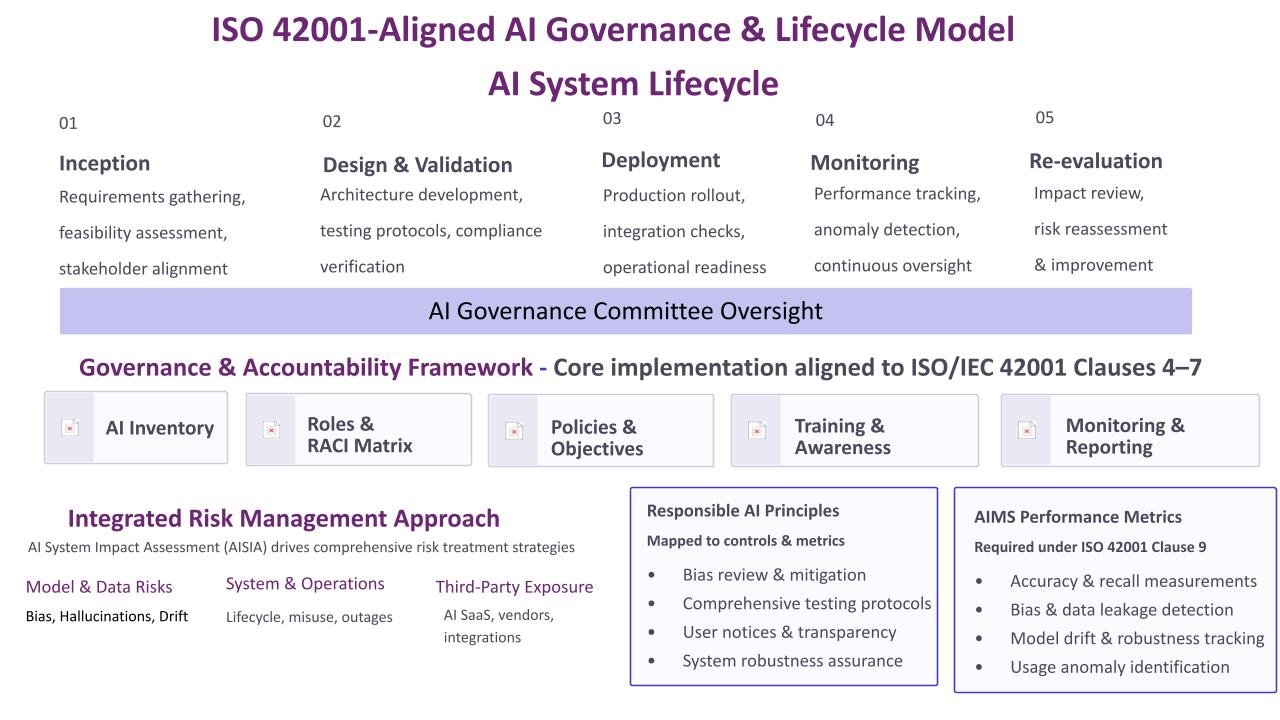
AI System Impact Assessment (AISIA)
AISIA is the point where AI governance becomes real. It is also where many organisations struggle.
We conduct AISIA in a way that supports decision-making and audit defence.
AISIA typically captures:
- intended use and prohibited use
- material impact on individuals and stakeholders
- model and data risks (bias, hallucination, drift)
- system and operational risks (misuse, outages, integration errors)
- third-party exposure (AI SaaS, sub-processors, training use)
- required controls, monitoring, and reevaluation triggers
AISIA outputs
- AISIA report per AI system
- AI impact register
- risk tiering and rationale
- inputs to risk register and Statement of Applicability
ISO 42001 certification readiness
Certification readiness is not a slide deck. It is evidence readiness.
We prepare organisations for certification audits through:
- Annex A mapping and applicability decisions
- justification for exclusions and scope boundaries
- control implementation with records and evidence
- internal audit (design and effectiveness)
- management review inputs and minutes pack
- audit handover file structure and evidence index
We do not sell certificates. We help you build an AIMS that auditors can validate.
Vendor and AI SaaS governance (Buy systems)
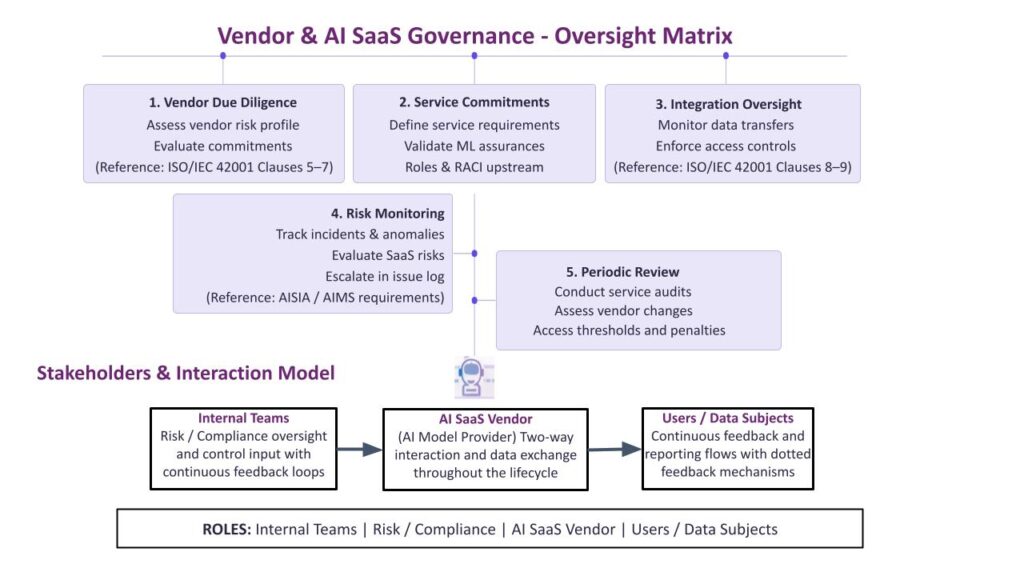
ISO 42001 applies to AI SaaS use. Vendor AI risk needs explicit governance.
Our vendor model covers:
- AI vendor classification and risk tiering
- AI-specific due diligence questions and evidence review
- contractual AI clauses (transparency, incident notification, change disclosure)
- integration oversight (data transfers, access controls, logs)
- monitoring of incidents, anomalies, and vendor changes
- periodic reviews and re-assessment triggers
This is designed for black-box systems where you do not control the model.
AI Without Guardrails Fails in Predictable Ways
- AI systems fail in structured, repeatable patterns
- Most enterprise AI risks come from integration, not the model
- Guardrails configured is not guardrails effective
Failure scenarios
- Prompt injection bypass
- RAG poisoning
- Copilot data overexposure
- Agentic unsafe actions
- Data leakage across sessions/logs
- Model drift in production
Policies are not enough. Controls must be tested and evidenced.
Read more AI Guardrails Testing and Validation for Enterprise AI Systems
AI Shared Responsibility Model (Critical for ISO 42001)
|
Layer |
Responsibility |
|
Model provider |
Base model only |
|
Platform (Copilot/API) |
Partial enforcement |
|
Enterprise |
Data, access, outcomes |
|
Integrator |
Implementation risk |
Key line:
Most AI risks are shared, but accountability sits with the enterprise.
Read More on AI Risk Assessment
Copilot and Enterprise AI Risk
- Copilots inherit enterprise permissions
- Retrieval may exceed user intent
- Connectors amplify exposure risk
- Guardrails depend on configuration
Examples:
- Over-permissioned access
- No prompt-level audit
- No escalation controls
- Lack of kill switch
From Controls to Evidence
- Controls exist, but evidence is weak
- Testing is missing in most AIMS implementations
We enable:
- AI red teaming
- Guardrail testing
- Evidence-backed audit
- Policy-based verdict (pass/warn/fail)
AIMS metrics and performance monitoring
ISO 42001 expects monitoring and evaluation of the AIMS.
We help define metrics that are measurable and usable, such as:
- accuracy / recall (where applicable)
- bias indicators (where applicable)
- leakage indicators and prompt security signals
- drift and robustness indicators
- usage anomalies and operational incidents
- corrective actions and time-to-close
Metrics feed management review. They also trigger reevaluation and change control.
Responsible AI principles (implemented, not posterised)
We keep principles practical. Principles must translate into controls and evidence.
Typical mapping:
|
Principle |
What it becomes in AIMS |
|---|---|
|
Accountability |
named owners, escalation paths, decision records |
|
Transparency |
user notices, documentation, limitation statements |
|
Fairness |
bias evaluation plan, review triggers, approvals |
|
Reliability |
validation, monitoring, drift thresholds |
|
Privacy & Security |
data controls, access controls, logging |
This prevents “principles-only” governance that cannot be audited.
Visuals to include on the page
Use two diagrams only. Keep them below the “How we implement” section.
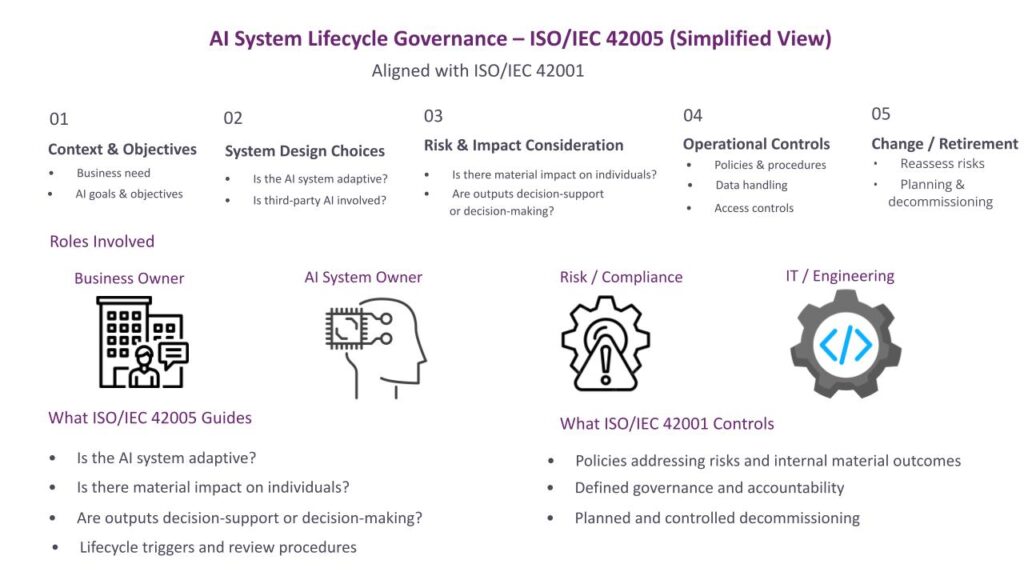
- ISO 42005 lifecycle guidance model
Caption: “Lifecycle governance view aligned with ISO 42001.” - Vendor & AI SaaS governance oversight matrix
Caption: “Oversight model for procured AI and AI SaaS tools.”
Who this is for
- organisations deploying GenAI internally
- enterprises using AI SaaS copilots or assistants
- teams formalising AI governance for audit readiness
- regulated environments with documented risk expectations
Organisations planning ISO 42001 certification
Why Pricoris
- implementation-first approach
- AISIA designed for decisions and audit defence
- vendor governance for AI SaaS and black-box systems
- templates built for traceability and evidence
- consulting and training delivered together when needed
Training options (if required)
-
We provide training aligned to implementation.
- ISO 42001 Awareness
- ISO 42001 Lead Implementer (3-day / 5-day)
- ISO 42001 Lead Auditor
- ISO/IEC 22989 concepts and terminology
- AISIA practitioner workshop
Training can be embedded into AIMS implementation to reduce cycle time.
Planning a certification? Our guide to ISO 42001 certification cost and timeline in India sets out what drives the fee, how long it takes, and when not to certify yet.
Frequently Asked Questions (FAQs)
1. Does ISO 42001 apply if we only use AI SaaS?
Yes. If you use AI systems, ISO 42001 governance still applies. Scope and controls will differ, but accountability, risk, vendor oversight, and monitoring remain required.
2. What is the difference between AISIA and AI risk assessment?
AISIA focuses on impact and consequences. Risk assessment focuses on likelihood, control effectiveness, and treatment. AISIA typically informs the risk assessment.
3. Can we implement ISO 42001 without seeking certification?
Yes. Many organisations implement for governance maturity and customer assurance. Certification is optional.
4. What do auditors look for in ISO 42001?
Clear scope. Control applicability logic. Evidence that controls operate. Traceability across the AIMS. Management oversight. Internal audit and management review records.
5. How long does ISO 42001 implementation take?
Typically 10–16 weeks depending on number of AI systems, vendor footprint, and governance maturity.
6. Does ISO 42001 cover GenAI and RAG systems?
Yes. The standard focuses on governance and lifecycle management. GenAI adds specific risks such as hallucination, leakage, and misuse that must be addressed through AISIA and controls.
7. How do you assess AI vendors under ISO 42001?
Using AI-specific due diligence, contract clauses, shared responsibility mapping, integration oversight, and periodic review. Evidence is key.
8. How does ISO 42001 relate to the EU AI Act?
ISO 42001 provides management system structure. The EU AI Act provides legal obligations based on risk classification. We help define what is covered by AIMS governance and what must be addressed through regulatory compliance controls.
8. Can ISO 42001 integrate with ISO 27001 and ISO 27701?
Yes. It aligns well with existing management systems. Many controls can reuse ISMS/PIMS mechanisms (policy, risk, supplier controls, audits).
9. What artefacts will we have at the end?
Typical outputs include scope, policy, objectives, RACI, AISIA reports, risk register, SoA, lifecycle procedures, vendor governance artefacts, internal audit records, and management review pack.
Ready to Explore ISO 42001 Consulting with Pricoris?
Discuss AIMS scope and applicability, review AISIA structure with sample outputs, and plan your ISO/IEC 42001 certification readiness with experts.
Book Now
Lorem ipsum dolor sit amet, consectetur adipiscing elit. Ut elit tellus, luctus nec ullamcorper mattis, pulvinar dapibus leo.