A consent notice under the DPDP Act is the statement a Data Fiduciary must give an individual before, or at the same time as, it asks for consent. Rule 3 of the DPDP Rules, 2025 requires the notice to be understandable on its own, to list each item of personal data with the specific purpose it serves, and to explain how the individual can withdraw consent, exercise their rights and complain to the Data Protection Board. Most notices fail on the itemised list and on the withdrawal route. This guide covers both, with a model structure you can adapt.
(A practical guide for teams building real DPDP compliance)
If there is one area where implementation goes wrong for most organisations, it is Notice and Consent.
The DPDP Act and the 2025 Rules look simple on paper, but once you start rewriting privacy notices or designing consent flows, the gaps become obvious.
Teams either copy GDPR templates, reuse legacy notices, or depend on UI patterns that simply do not meet India’s requirements.
This guide explains, in plain language, what the law actually expects, and the mistakes you want to avoid.
1. Start with Rule 3: The Core of India’s Notice Requirements
Rule 3 of the DPDP Rules 2025 lays out the mandatory ingredients of a valid notice.
A DPDP-compliant notice must clearly state:
✔ Identity and contact details of the Data Fiduciary
A generic email or a legal name buried in the footer will not suffice.
Teams must explicitly mention:
- Legal entity name
- Physical or registered address
- Contact of Grievance Officer
✔ Itemised list of personal data collected
This is one of the most important differences from GDPR.
DPDP requires a specific, item-wise list of what you collect.
“Information you provide” or “data such as contact details” is no longer acceptable wording.
✔ Purpose of processing: specific, not broad
You cannot write “improve our services”, “enhance experience”, “product development”, “analytics”, or “marketing” as a combined purpose.
Every purpose must be single, clear, and connected to a specific data element.
✔ Rights of the Data Principal
Not just access or correction: include updating, completion, erasure, withdrawal, and nomination.
✔ Consent withdrawal mechanism
Rule 3 requires that the notice “shall contain the manner for withdrawal of consent”.
This means the UI cannot hide the withdrawal link behind:
- multiple steps
- email requests
- customer support calls
- banners that “acknowledge your choice”
✔ Language accessibility
Every notice must be available in English or any language from the Eighth Schedule of the Constitution.
This is a statutory requirement.
2. The Most Common Mistake: Not Providing an Itemised Data List
Notice statements like:
“We collect information such as your name, contact details and other information you provide.”
…will fail under Rule 3.
DPDP expects itemisation such as:
- Name
- Mobile number
- Email ID
- Address
- Device information (model, OS, IP address)
- Payment confirmation details
- Chat transcripts (if applicable)
If your system collects 15 data points but your notice lists only 4, the notice becomes invalid.
This is the most frequent mistake across HR portals, CRMs, mobile apps, and website signup forms.
3. UX Expectations: DPDP Requires ‘Understandable, Accessible, Human-Readable’ Notices
A notice is not compliant if:
- it is hidden behind a link
- written in dense legal language
- placed below the fold
- delivered only after signup
- includes vague or bundled purposes
- requires clicking through multiple screens
- shows the notice after consent is already taken
A DPDP-compliant notice must appear before data collection, clearly visible, and easy to read.
Small teams often underestimate this.
Large companies often over-engineer it with 700-word legal text.
Both approaches fail.
4. Consent Under DPDP: A Very Different Concept from GDPR
DPDP defines valid consent as:
Free, specific, informed, unconditional, unambiguous and given through clear affirmative action.
Let’s break down the parts companies get wrong.
A. “Unconditional” Consent: Frequently Misunderstood
“Unconditional” does not mean:
- the company cannot deny service if consent is refused
- the user gets full access even if the purpose is essential
It means:
- You cannot force additional, unnecessary consent as a condition for the service.
Example:
A food delivery app can require location access for delivery.
It cannot require access to contacts “to improve experience”.
B. No “Legitimate Interest”: Only “Legitimate Use”
GDPR’s Legitimate Interest does not exist under DPDP.
DPDP uses a closed list of Legitimate Use grounds under Section 7:
- voluntary data given for a specific purpose
- compliance with law
- employment purposes
- medical emergencies
- fraud detection
- court orders
- public interest functions
If your GDPR programme depends heavily on “Legitimate Interest”, you must redesign your legal basis mapping.
C. Consent Withdrawal Must Be “Equal Ease”
Another major mistake.
DPDP requires that withdrawing consent should be as easy as giving it.
Meaning:
- no hidden links
- no “email us to withdraw”
- no multi-step processes
- no mandatory calls with customer support
- no refusal unless service genuinely depends on data
“Equal ease” is a real UX requirement, not an aspirational one.
5. Difference Between DPDP and GDPR Notice Patterns
Clients often assume that GDPR notices can be reused.
This almost always fails.
DPDP vs GDPR: Key Notice Differences
| Requirement | GDPR | DPDP (Stricter) |
|---|---|---|
| Itemised data list | Recommended | Mandatory |
| Notice language | Plain language | English or Eighth Schedule language |
| Purpose | Can be grouped | Must be specific & separate |
| Legal bases | 6 bases including Legitimate Interest | Consent + limited Legitimate Use grounds |
| Consent withdrawal | Reasonable ease | Equal ease required |
| Children | Parental consent + age verification | No tracking, profiling, targeted ads |
| Delivery timing | Before or at data collection | Before collection & accessible anytime |
6. The 10 Most Common Mistakes Organisations Make Under DPDP
Mistake #1: Using GDPR notices without localisation
DPDP needs specific formats and itemisation.
Mistake #2: Taking consent before showing notice
Illegal under Rule 3.
Mistake #3: Bundled consent
E.g., “I agree to the Privacy Policy and Terms”.
This is invalid.
Mistake #4: Vague purposes
“Improve services”, “marketing and analytics”, “product enhancement”: all invalid.
Mistake #5: Not offering withdrawal with equal ease
If your UI hides withdrawal behind layers, it fails.
Mistake #6: Not showing notice in accessible languages
At least English or an Eighth Schedule language is mandatory.
Mistake #7: No audit trail of consent
Logs need to be retained for at least one year (Rule 6).
Mistake #8: No separate notices for children’s data
DPDP’s child-protection rules are stricter than GDPR.
Mistake #9: Using pre-ticked or implied consent patterns
DPDP requires affirmative action.
Mistake #10: Not updating notices when purposes change
DPDP requires timely communication of any modifications.
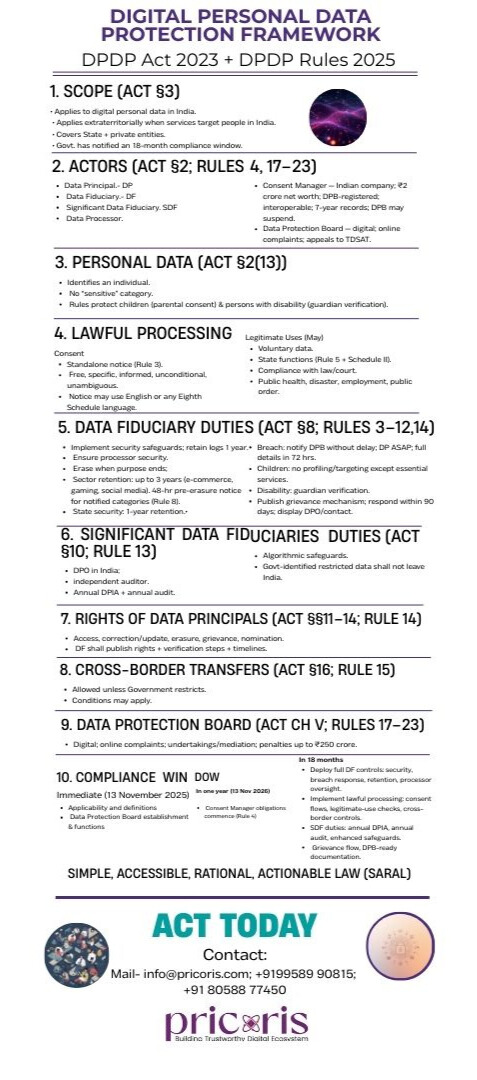
7. A Model Consent Notice Structure
Every consent notice under the DPDP Act should cover the elements below, in this order, at the point where personal data is collected.
| Element | What to write | Source |
|---|---|---|
| Who you are | The legal name of the Data Fiduciary and the contact for questions about its processing | Section 8(9) and Rule 9 |
| Each item of personal data | An itemised list: name, mobile number, email address, delivery address, and so on | Rule 3 |
| The purpose for each item | A specific purpose, and the goods, services or uses it enables | Section 5 and Rule 3 |
| How to withdraw consent | A direct link, and any other means, as easy to use as giving consent | Section 6(4) and Rule 3 |
| How to exercise rights | The route for information, correction, erasure, nomination and grievances | Section 5 and Rule 3 |
| How to complain to the Board | The route to the Data Protection Board of India | Section 5 and Rule 3 |
| Language | English, with the option to read it in any language in the Eighth Schedule | Section 5(3) |
A short example, for an online shop:
[Company legal name] will use the following personal data to create your account and deliver your orders: your name, mobile number, email address and delivery address. We will use your mobile number to send order updates by SMS. You can withdraw your consent at any time at [consent link], as easily as you gave it. To see, correct or erase your data, or to nominate someone to act for you, visit [rights link] or write to [contact email]. If you are not satisfied with our response, you may complain to the Data Protection Board of India at [Board link]. This notice is available in English and [second language].
The notice is also where individuals first learn about their rights as data principals under the Act. If your notices were written for the GDPR, our guide on how to choose a DPDP consultant in India explains what a sensible rewrite should and should not include, and our DPDP consulting page covers how we run notice and consent work.
8. Practical Checklist for Teams
DPDP Notice & Consent Checklist
✔ Notice shown before any data collection
✔ Itemised list of every data field collected
✔ Purpose for each data field is specific
✔ Consent is explicit and affirmative
✔ No bundled or vague consent
✔ Withdrawal link provided with equal ease
✔ Notice available in English or Eighth Schedule language
✔ Separate notice for children (if applicable)
✔ Log retention configured for 1 year (Rule 6)
✔ Notice updated whenever purpose changes
✔ Consent Manager integration documented (if used)
9. Final Takeaways
DPDP’s approach to Notice and Consent is stricter, more structured, and more user-focused than most companies expect.
If there is one area to get absolutely right, it is this, because invalid notices automatically make your processing unlawful.
This is where most compliance failures will happen, and where the DPB is most likely to investigate.
Frequently asked questions
It is the statement a Data Fiduciary must give before, or together with, a request for consent. It must list the personal data to be collected and the purpose for each item, and explain how to withdraw consent, exercise rights and complain to the Data Protection Board.
Rule 3 requires the notice to be understandable independently of any other information. A link to a long privacy policy is not enough on its own; the notice must stand alone at the point of collection.
An itemised description of the personal data, the specific purpose for each item, the way to withdraw consent, the way to exercise rights, and the way to complain to the Data Protection Board.
The individual must be able to read it in English or in any language listed in the Eighth Schedule to the Constitution.
Yes. Section 5(2) requires a notice, as soon as reasonably practicable, to individuals who gave consent before the Act commenced.